Blog
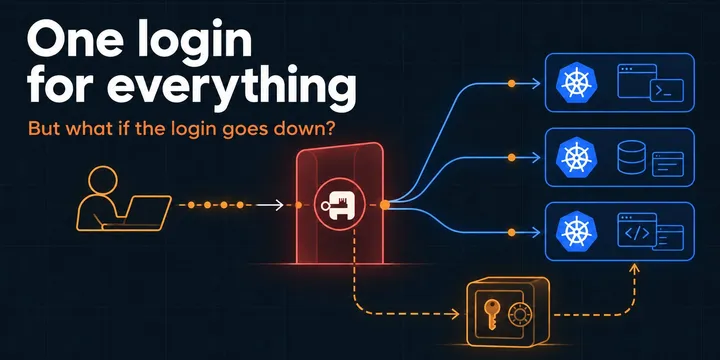
One login for everything, and a spare key under the mat
For a long time, giving someone access to our Kubernetes clusters went like this: create a ServiceAccount, write a Role and a RoleBinding for whatever that person needed, mint a token, wrap it in a ku...
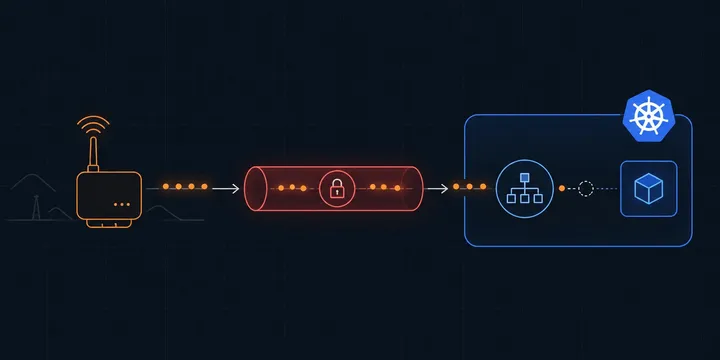
LoRaWAN over WireGuard looked like a weekend job
Somewhere out there, one of our Edgepilot LoRaWAN® gateways sits behind a mobile carrier's CGNAT, quietly having its public IP and port rotated out from under it. Its job is to forward LoRa packets ov...
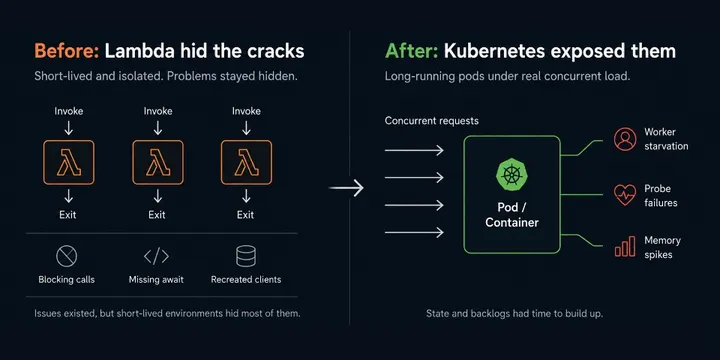
What Lambda let us get away with
I already wrote about the AWS incident that pushed us onto Kubernetes. That post was about the infrastructure side: the account lockout, the blast radius, the move to a self-managed k3s cluster. This...
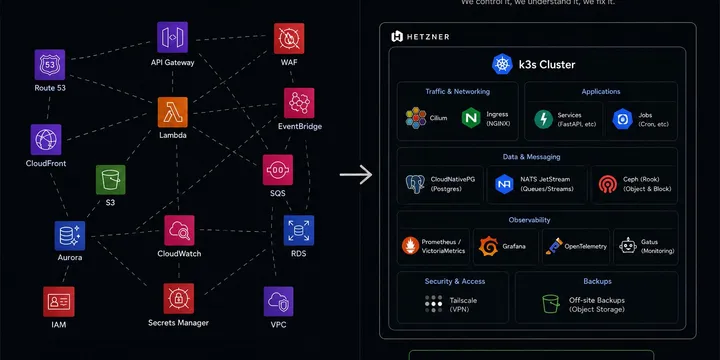
The AWS incident that made us move everything to Kubernetes
On November 20th 2025, around 21:00, I suddenly started getting alerts that basically every Trackpac production service was down at the same time. DNS (it's always DNS), Lambda functions, APIs, databa...